Apparently, human beings are hard-wired to detect patterns. Sometimes this is
good, but sometimes it can be
too effective, or
misleading, or
subject-to-multiple-interpretations... A cynic might rewrite it as:
Humans are hard-wired to detect patterns, even when the patterns aren't there...
Patterns are very important in security, or, to put it another way: the hiding of patterns is often very important in security. Encryption is a good example of a way of hiding the patterns of ASCII-encoded text data and making them look slightly more noise-like. 'Obfuscation' is that wonderful word for hiding something in plain sight. I always remember something that was drilled into me when I worked on audio encoding:
The better the coding scheme, the more the output looks like noise.
And this hooks very nicely into the way that people use entropy as a way to find encoded data - plain program code has low entropy, but encrypted passwords (or other important/valuable data) have high entropy. So scanning code for high entropy sections would seem to be a good way of finding interesting encrypted data...
Unfortunately, one of the obvious things to do when you start to protect data with encryption is to hide it in similar data. Encryption is not the only way to increase the entropy of program code, of course, just applying a simple compression scheme would also work. This 'one action leads to a corresponding follow-up action, which then leads to another action...' is the 'climbing a ladder' escalation analogy that can be used to model all sorts of interchanges.
Puzzles are interesting because they can train you to look at problems in many different ways, and breaking assumptions - one of the other things that humans are very good at is making assumptions, of course.
So, let's look at one of the puzzles on the
Nullcon 2020 badge (and the
answers), and see how it encourages potential puzzle solvers (like security analysts and cryptographers) to think laterally.
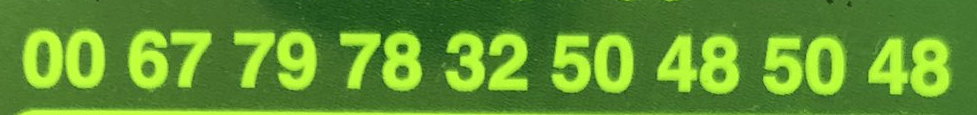
Here's what part of the top of the badge looks like:
(There's something about the look of 'fluorescent green plastic' that makes it appear super-cool!)
Puzzle setters like myself know that there are clues that give away typical encodings that are used for text, so any numbers between 46 and 122 (decimal) would tend to suggest an ASCII encoding (A-z, plus 0-9 plus '.' and '/'), which would be confirmed by having lots of '32's indicating spaces. In this case, the initial number is '00', which is deliberate misdirection, and is based on people initially looking at the beginning and ending of sequences - putting the 32 mid-sequence kind of hides it amongst the other numbers.
So the '00' is hopefully going to cause some people to immediately reject this as being ASCII-encoded text, but then if they look closer, they will see the '32' and note that all the other numbers are between 48 and 122... Which means that it probably is ASCII-encoded text, but that the first character is different or special in some way. One thought at this point might be that this is an index: the first piece of encoded text might be preceded by a zero, and so other encoded text would then be examined to see if the initial numbers were 01, 02 03, etc. But the other number puzzles on the badge do not follow this sequence (so one obfuscation method that a puzzle setter could potentially use would be to deliberately offset ASCII-encoded text so that the first number is an ascending index or offset...) and so there must be something else about the number '00'. Looking it up on an ASCII table quickly reveals the secret: 00 is the decimal number that represents the archaic non-printing 'NULL' character, and given the name of the conference for this badge (Nullcon!), it is obvious that the Null character is being used to replace four ASCII numbers with a single shortcut number!
One can imagine a puzzle setter who exploits this to encode other words with appropriately similar extensions using the ASCII characters outside of the ./A-z, 0-9 (46-122) range. If the fictional conference called 'DevCan' wanted a badge, then this could be encoded with 127 (character for 'DEL' (delete)), then 08 ('backspace'), then 11 ('VT', the 08 ('backspace'), then 24 (character for 'CAN' (cancel)). Thus giving 127 08 11 08 24 for encoding DevCan. That 127 is a dead giveaway, so I suspect that the hex versions would be used instead: 7F 08 0B 08 18.
For Hex-encoded ASCII, then the numbers that people look for are 2E to 7B (./0-9A-z), so those two 08s and the 18 are good misdirection!
If the puzzle solver approaches things from the opposite end of the sequence (often a good technique to try), then the last four numbers are all inside the 0-9 range of 48-57 (decimal), and so are obviously numbers. Decoding them to '2020' is another strong clue that this is ASCII-encoded text.
Finally, there's the 32, which is like a waving red flag to anyone who is looking for ASCII-encoded text! One approach that a puzzler might take would be to replace this with another character: 00 (Null) being one candidate. But in this case, 00 is already used, so another character would be used. Using 00 (Null) as a replacement character for 'Space' might be something that a specific puzzle setter has used previously, of course, and so knowing who set the puzzle might be useful. Conversely, puzzle setters might strive to avoid using the same obfuscation methods more than once.
One difference between a puzzle and real world decoding is that puzzle setters like to give clues. The 32 in the middle of this sequence is one example, but for a conference called Nullcon, with a badge that has the word 'Nullconium' as well as 'Nullcon' written in a weird 'falling-over' books font, then there are lots of pointers to 'Nullcon' being a likely candidate for some encoded text on the badge - especially given the 'Periodic Table tile' / 'Top Trumps card' metaphor of the badge design.
If you have read this far, then you should now have had a glimpse of how puzzles like the Nullcon badge can encourage you to take an
oblique look at problems, and thus may help you to solve your next challenge in an inventive and unusual way. And the world definitely needs
novel solutions!
---
If you find my writing helpful, informative or entertaining, then please consider visiting the following link for my Synthesizerwriter alias (I write several blogs, but it makes sense to only have one 'Coffee' donation link!):


 Synthesizerwriter's Store (New 'Modular thinking' designs now available!)